Blog
Cyber Security
The TARA Arrives, Its References Don't
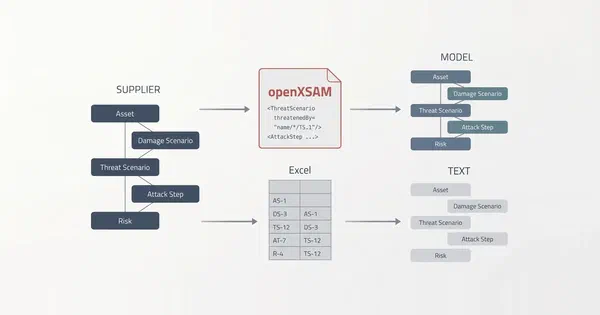
Why a TARA loses its references on the way from supplier to OEM, what openXSAM gets back, and why that takes a model.
Read Article Jens Bühl
8 min read
Holistic protection and seamless traceability for cybersecurity, functional safety, and the Cyber Resilience Act
Overview

Methodological excellence and tailored tools for model-based system and software engineering.
Overview

Enterprise software from a single source: AI integration, legacy migration and full-stack development — cost-efficiently and sovereignly hosted.
Overview

Cyber security in engineering: articles on threat analysis (TARA), security by design and ISO/SAE 21434 from the practice of itemis security experts.
Format
Why a TARA loses its references on the way from supplier to OEM, what openXSAM gets back, and why that takes a model.
Read Article
Jens Bühl
8 min read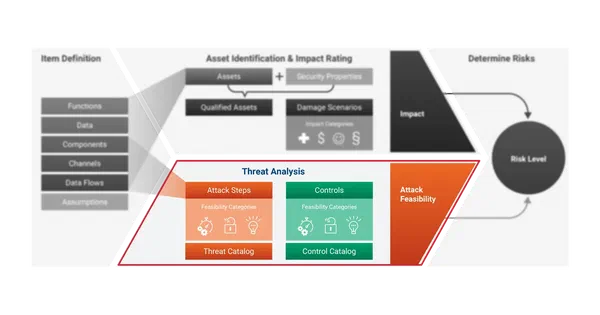
Threat scenario, attack path and attack feasibility belong together: what makes a scenario, why the path gets rated, and how the method shifts the result.
Read Article
Jens Bühl
13 min read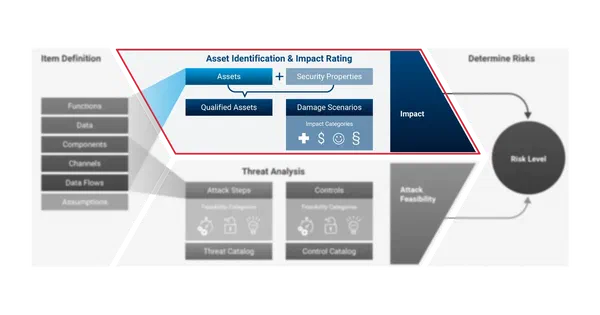
Asset identification and impact rating supply one half of the risk value: when an element of the item becomes an asset, whose damage a damage scenario describes, why the safety rating is not security's to set alone, and what keeps ratings comparable across projects.
Read Article
Jens Bühl
15 min read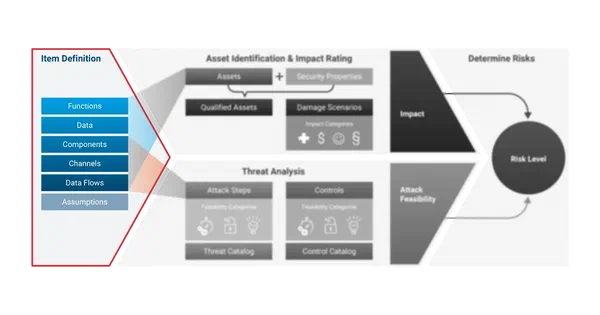
The Item Definition sets the quality ceiling for the whole TARA — what abstraction level is right, why SBOM mapping forces a minimum resolution, and why a living model is the foundation for API and MCP integrations.
Read Article
Jens Bühl
9 min read
From risk definition to a living TARA: a 7-part guide to systematic cyber risk assessment, with direct mappings to CRA, ISO/SAE 21434, and IEC 62443.
Download Whitepaper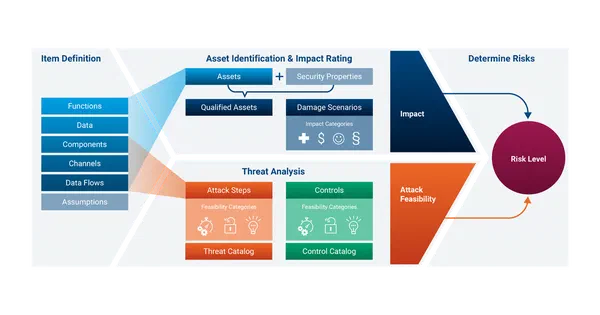
A TARA is not a threat catalogue — it is an auditable record of risk decisions: what it involves, how the process works, and when Excel reaches its limits.
Read Article
Jens Bühl
6 min read
How AI assistants reduce TARA creation from weeks to hours — and turn your threat analysis into a real competitive advantage.
Watch Webinar
Jens Bühl
Learn how TARA automation with itemis SECURE (formerly YAKINDU Security Analyst) makes cybersecurity processes in the automotive industry fundamentally more efficient.
Watch Webinar Jonathan Mohring
Your TARA is a compliance document. It should be the operational brain of your CSMS. This whitepaper shows how a Living Digital Thread transforms static security artifacts into a continuous, data-driven lifecycle operation.
Download Whitepaper
How leading OEMs and Tier-1 suppliers unite Functional Safety and Cyber Security enterprise-wide — without disrupting proven engineering environments.
Download Whitepaper
itemis SECURE is now available on the web — collaborate on cybersecurity projects simultaneously from any device, just like Google Docs.
Watch Webinar
With software-defined vehicles, the start of production is no longer the end of development — a holistic approach to security is now essential.
Watch Webinar
Dirk Leopold
Dynamic-TARA by VicOne and itemis automates vulnerability detection and feeds it directly into comprehensive threat analysis and risk assessment.
Watch Webinar
In the EU, UN Regulation No. 155 applies to new motorcycle types from December 2027 and to all types from June 2029 — discover how to prepare your organization for the homologation challenge and emerging cyber threats.
Watch Webinar
Dirk Leopold
Understand the present challenges in risk management for OEMs and suppliers and learn how best-of-breed toolchains and knowledge graphs deliver real value.
Watch Webinar
Dirk Leopold
How threat analyses (TARAs) and secure data exchange protect the EV ecosystem — from charging infrastructure to the vehicle itself.
Watch Webinar
Dirk Leopold
Learn how model-based TARA tooling combined with knowledge graphs enables CSMS automation for type approvals and gives you the competitive edge.
Watch Webinar
Jonathan Mohring
Learn how to efficiently manage the TARA process, keep your TARAs up-to-date, and apply the 20-50-90 Rule to significantly reduce cybersecurity spend.
Watch Webinar
Dirk Leopold
ISO/SAE 21434 raises the bar for automotive cybersecurity — from company-wide CSMS governance to threat analysis and product-level security controls. This guide, co-authored by itemis and Deloitte, walks you through every clause that matters.
Download Whitepaper
Learn why transitioning from spreadsheet-based TARAs to automated processes is essential and how to harmonize your TARA landscape across OEMs and suppliers.
Watch Webinar
Jens Bühl
For CFOs and auditors, a new family of threats and controls is emerging: cybersecurity controls and audit reports for their companies' connected products.
Watch Webinar
Dirk Leopold
Get an overview of threat and control catalogs that speed up your ISO/SAE 21434 compliant TARAs throughout the entire vehicle lifespan.
Watch Webinar
Jens Bühl
UN Regulation 155 and ISO/SAE 21434 require the entire automotive industry to ensure security over the entire lifespan of the vehicle.
Watch Webinar
UN Regulation 155 and ISO/SAE 21434 require the entire automotive industry to ensure security over the entire vehicle lifespan — from development through maintenance to decommissioning.
Watch Webinar
Dirk Leopold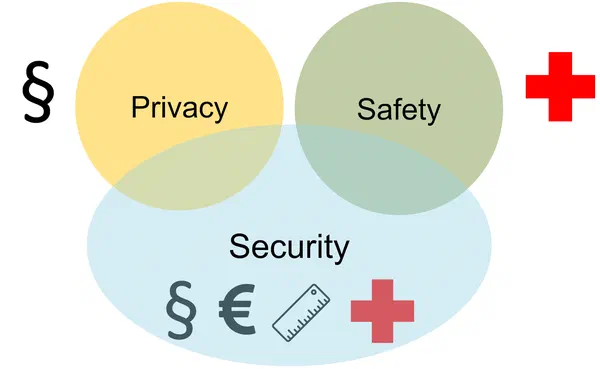
In the automotive domain, security is becoming more and more important – especially for the new generations of connected, (semi-)autonomous vehicles. Learn how to develop a secure system design and which additional security challenges may arise.
Read Article
Dirk Leopold
9 min read
In times of Spectre and Meltdown it's totally clear that security is a big engineering challenge. Learn more about safety and security in this post.
Read Article
Dirk Leopold
8 min read
The increased share of software solutions places high demands on Automotive Security. But what changes are coming for the industry and manufacturers?
Read Article
Dirk Leopold
5 min read